Delegated credentials: Improving the security of TLS certificates
Nov 1, 2019Alex Guzman, Kyle Nekritz, Subodh Iyengar
Summary
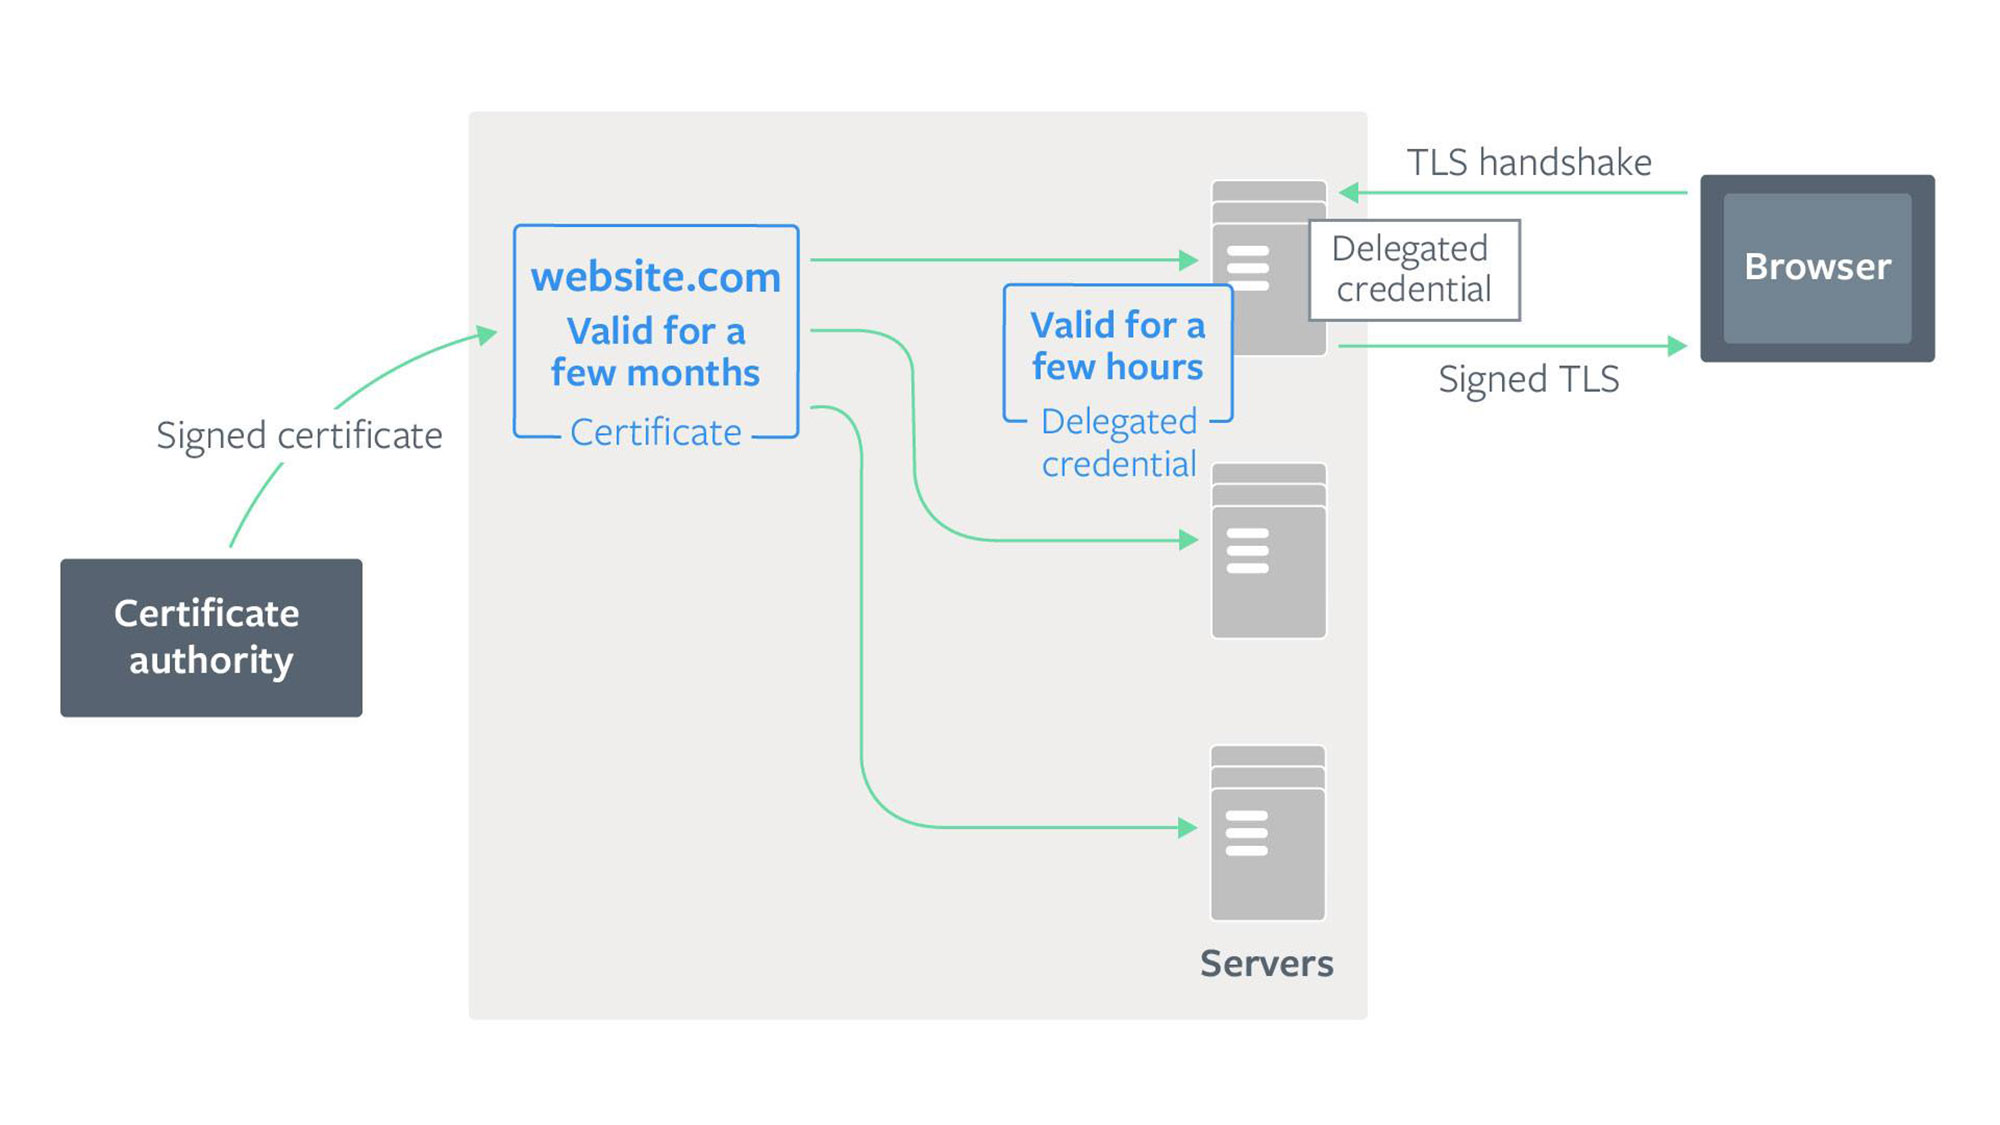
This post introduces and explains the concept of 'delegated credentials,' a new extension to the TLS protocol being developed with industry partners. It addresses the challenges of managing TLS certificates at scale, particularly the security risks associated with long certificate lifetimes and the limitations of traditional revocation mechanisms. Delegated credentials offer a way to significantly shorten certificate lifetimes (to hours or days) by allowing servers to sign their own short-lived credentials using their primary certificate, thereby improving security and reducing reliance on revocation without impacting reliability. The post also highlights Meta's implementation of this in Fizz and provides a test endpoint.