Introducing Pull Request Annotation for CodeQL and Dependency Scanning in GitHub Advanced Security for Azure DevOps
Oct 17, 2024Michael Omokoh
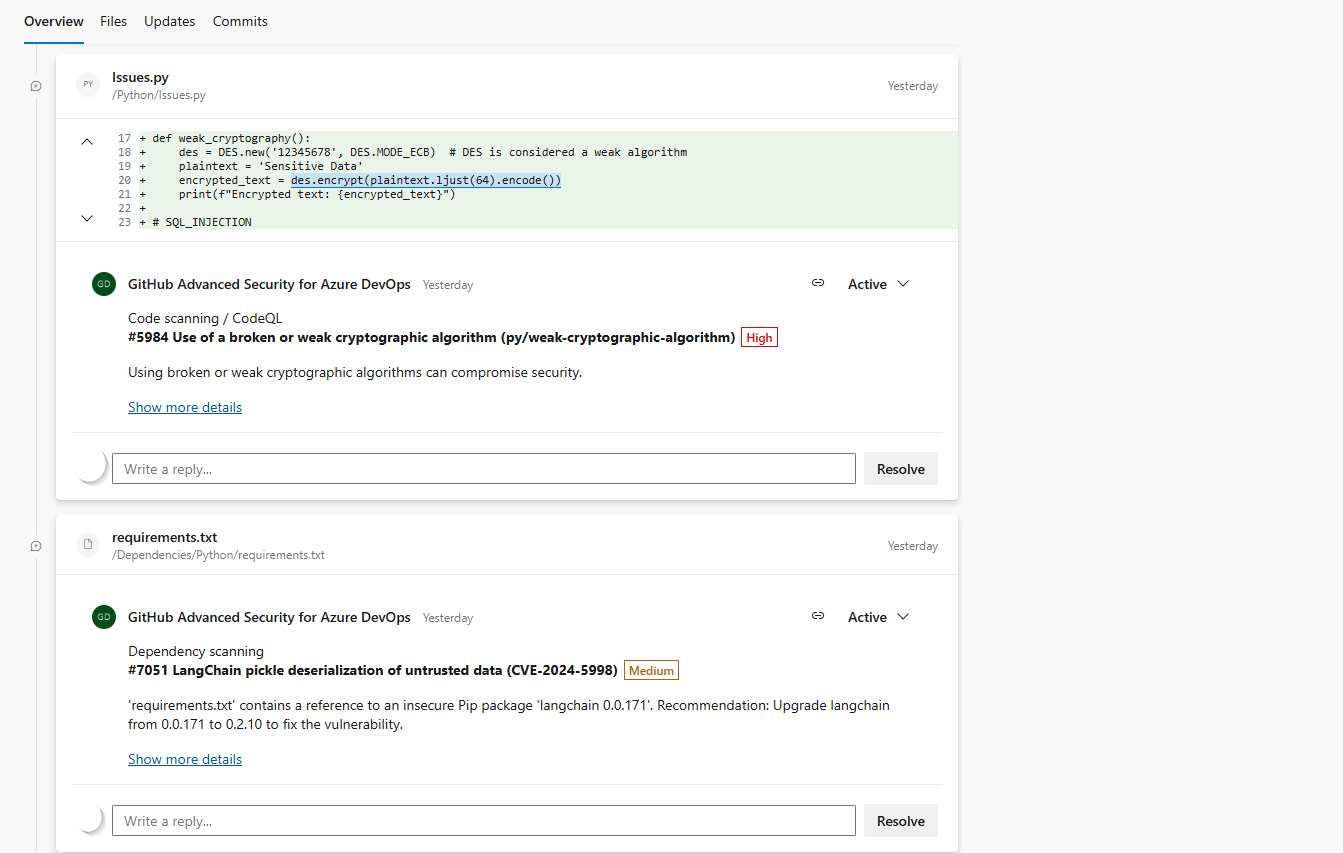
Summary
This post introduces Pull Request (PR) Annotation for CodeQL and Dependency Scanning within GitHub Advanced Security for Azure DevOps. This feature automatically scans code and dependencies during a Pull Request, reporting any found security issues directly as annotations on the PR interface. This provides developers with immediate feedback on potential vulnerabilities, facilitating quicker fixes and more efficient peer reviews, thereby integrating security directly into the development workflow and CI/CD pipeline.
More from the Azure Pipelines Supply Chain Security trail
- Axios npm Supply Chain Compromise – Guidance for Azure Pipelines Customers
- Automate your open-source dependency scanning with Advanced Security
- One Pipeline to Rule Them All: Ensuring CodeQL Scanning Results and Dependency Scanning Results Go to the Intended Repository
- April Patches for Azure DevOps Server and Team Foundation Server
- February patches for Azure DevOps Server