Google Pay inside sandboxed iframe for PCI DSS v4 compliance- Google Developers Blog
Jun 10, 2025Dominik Mengelt, Matthew Class
Summary
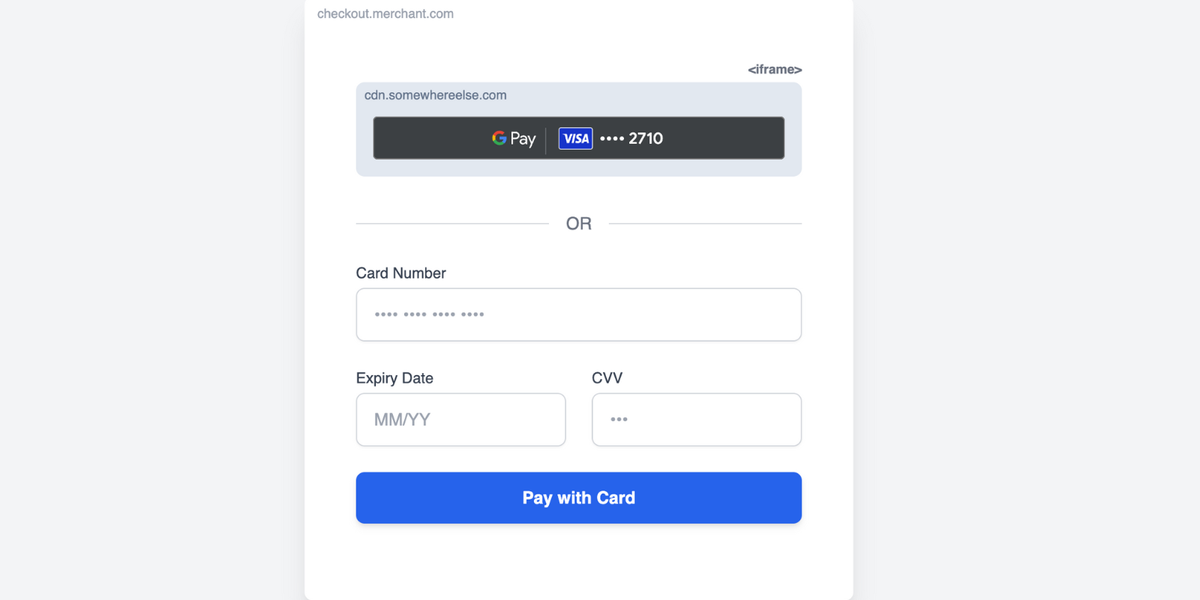
This post introduces a method for integrating Google Pay into a PCI DSS v4 compliant checkout page by using a sandboxed iframe. It details the necessary sandbox attribute values (`allow-scripts`, `allow-popups`, `allow-same-origin`, `allow-forms`) and the `allow='payment'` attribute for the iframe. It also highlights Shopify's successful implementation and certification using this approach, emphasizing how it addresses the requirement for managing payment page scripts.